Confidential Computing for AI: How GPUs Process Private Data Without Exposing It to the Cloud Host
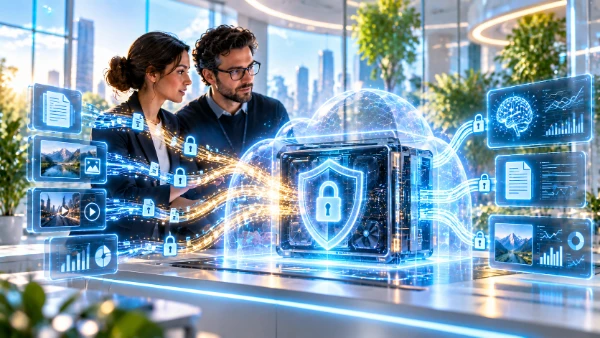
Artificial intelligence increasingly works with information that organisations cannot afford to expose: medical records, financial transactions, legal documents, customer conversations, proprietary research and private business data. Encryption already protects much of this information while it is stored or moving across a network, but AI creates a more difficult problem because data normally has to be available in readable form while a processor is using it. Confidential computing addresses this gap by creating a hardware-protected environment in which sensitive information can be processed while remaining isolated from the underlying cloud host. Modern confidential GPUs extend this protection to AI workloads, allowing models to analyse private information without giving ordinary host software, administrators or the hypervisor direct access to the unencrypted data being processed.
How Confidential Computing Protects AI Data During GPU Processing
Traditional cloud security usually focuses on two states of information. Data at rest can be encrypted on a disk or in object storage, while data in transit can be protected with encrypted network connections. The difficult stage is data in use. A conventional processor normally needs access to readable information while calculations are being performed, which creates an additional area that must be protected. Confidential computing changes this arrangement by placing the workload inside a Trusted Execution Environment, commonly shortened to TEE. This is a hardware-isolated area designed to keep the workload and its memory separate from software outside the protected environment.
For AI workloads, protecting only the central processor is not enough. Large language models, computer vision systems and many other machine-learning applications depend heavily on GPUs because these processors can perform large numbers of calculations in parallel. Sensitive information may therefore move from protected CPU memory to GPU memory before inference or training begins. Confidential GPU technology extends the trusted environment to the accelerator itself. Supported GPUs use security features built into their hardware and firmware to isolate confidential workloads and protect information while calculations are taking place.
The important distinction is that confidential computing does not simply ask a cloud provider to promise that administrators will not inspect customer data. The security boundary is enforced by hardware. Encryption keys used to protect the confidential environment are designed to remain within protected hardware rather than being exposed to the host operating system or hypervisor. The cloud operator still owns and manages the physical machine, but the architecture reduces the amount of sensitive information that ordinary host-level software can inspect. This is particularly valuable when an organisation wants the computing power of shared cloud infrastructure without treating every layer of that infrastructure as fully trusted.
What Actually Happens When Private Data Reaches the GPU
A confidential AI session usually begins inside a confidential virtual machine. Sensitive input is decrypted only within this protected environment rather than in the normal host operating system. Before the GPU is trusted with the workload, its identity, firmware and security state can be checked through attestation. Attestation provides cryptographic evidence about the hardware and software configuration. If the expected security conditions are not met, an organisation can prevent sensitive information, model weights or encryption keys from being released to that environment.
Once the GPU has been verified, information can be transferred from the protected CPU environment to the confidential GPU through a secured connection. NVIDIA’s confidential computing design supports protected communication between the confidential virtual machine and compatible GPUs. The GPU then performs the same type of mathematical work required for AI inference or training, but the relevant memory and execution environment remain isolated from the normal host. A cloud administrator with access to the surrounding server should therefore not be able to simply inspect GPU memory and read the customer’s prompts, datasets or model parameters.
After processing, the result returns to the protected virtual machine, where the application decides what should happen next. It might encrypt the result before storing it, return it through a secure connection or pass it to another approved component. This matters because confidential computing protects the execution environment rather than automatically making every application secure. If an application deliberately sends sensitive information to an external service, confidential hardware cannot prevent that behaviour. The application, model, access rules and data-handling policy must still be designed correctly.
Why Confidential GPUs Matter for Real AI Workloads
One of the clearest uses for confidential GPU computing is AI inference on private organisational data. A company may want a large language model to summarise contracts, analyse customer support records or answer questions using internal documents. Those tasks can contain information that should not be visible to unrelated infrastructure administrators. Running the workload inside a confidential CPU and GPU environment reduces the number of components that must be trusted with the unencrypted material. The model can still perform its calculations, but the sensitive inputs and model data are better isolated from the surrounding host.
Healthcare provides another practical example. Medical organisations may use AI to analyse scans, clinical notes or other records containing personally identifiable information. Financial institutions face similar concerns when models process account records, fraud signals or transaction histories. Confidential computing cannot replace regulatory controls, identity management or good data governance, but it can add another layer of technical separation. Instead of relying only on permissions around the server, sensitive calculations are carried out within a hardware-enforced security boundary.
Confidential GPUs can also protect the AI model itself. For many businesses, trained model weights, fine-tuning data and inference logic are valuable intellectual property. A company may want to run its model on external infrastructure without exposing the model to the operator of that infrastructure. Confidential computing can therefore protect information in both directions: the customer supplying private data can reduce exposure of that data, while the organisation supplying the model can reduce exposure of its proprietary AI assets. This makes the technology relevant to shared AI services, research collaborations and commercial models deployed outside an owner’s own data centre.
Where Confidential AI Can Change Data Sharing
Confidential computing becomes particularly useful when several organisations need to work with the same AI system but do not want to reveal their raw data to one another. Consider hospitals collaborating on medical research, banks comparing fraud patterns or companies jointly training a specialised model. Under a conventional arrangement, one organisation may have to receive and control the combined information. A confidential environment can instead provide an agreed location where approved code processes the data while the participating organisations retain stronger control over what is exposed.
Attestation plays an important role in these arrangements because it allows a data owner to check the execution environment before releasing information. The owner does not simply need to trust a written statement that a particular machine is configured securely. Cryptographic evidence can be used to confirm characteristics of the confidential virtual machine and compatible GPU. Policies can then be created so that encryption keys or datasets are released only when the expected measurements and security state are verified. This changes confidential computing from a passive encryption feature into a mechanism for deciding where sensitive data is allowed to become usable.
Google Cloud provides a practical example of this model. Its Confidential Space service supports confidential workloads designed for situations where different parties need to process sensitive information without handing unrestricted access to one another. In April 2026, Google announced general availability of Confidential Space support for H100 GPU workloads, and in September 2026 it announced generally available H100 support with Intel Trust Authority attestation. These developments show that confidential AI is moving beyond isolated demonstrations and into cloud services that organisations can deploy for real workloads.
What Confidential GPU Computing Can and Cannot Protect in 2026
By 2026, confidential GPU computing is available with real commercial hardware rather than existing only as a research concept. NVIDIA documents confidential computing support across several current accelerator families. Its confidential container documentation lists H100 and H200 for single-GPU use, protected multi-GPU configurations for H100 and H200, and support involving newer B200 and B300 hardware. RTX PRO 6000 is also included for supported single-GPU configurations. Exact availability still depends on the cloud service, region, virtual machine type, driver and security configuration.
Google Cloud currently documents NVIDIA H100 GPUs with its A3 High confidential virtual machines using Intel TDX. It also documents G4 confidential virtual machines that combine AMD confidential computing technology with NVIDIA RTX PRO 6000 GPUs. Microsoft Azure offers the NCCadsH100v5 family, combining fourth-generation AMD EPYC processors using SEV-SNP with NVIDIA H100 Tensor Core GPUs. In that configuration, the protected execution environment covers the confidential virtual machine and the attached GPU so that protected workloads can transfer data and computation to the accelerator.
Availability should not be confused with universal support. Confidential GPU configurations remain more restricted than ordinary GPU machines. Specific regions, machine sizes and operating systems may be required, while some advanced multi-node configurations are not available through every cloud service. Google, for example, documents restrictions for its confidential NVIDIA GPU virtual machines, including limitations around certain multi-node workloads. Organisations planning large training clusters therefore need to check whether the security mode they require is compatible with the scale and networking design of the intended AI workload.
The Security Limits Organisations Still Need to Understand
Confidential computing significantly narrows the group of infrastructure components that can access sensitive information, but it does not guarantee that an AI application is safe in every respect. The code running inside the trusted environment must eventually work with the usable data. If that code contains a vulnerability, exposes information through an API or has been deliberately designed to copy data elsewhere, hardware isolation alone cannot correct the problem. Confidential computing therefore works best as one part of a wider security model that includes controlled software, strong authentication, restricted network access and careful management of encryption keys.
Attestation also needs to be treated as an operational security control rather than a one-time checkbox. NVIDIA recommends attestation as part of confidential GPU deployments because the process verifies that the expected hardware and software state is present before protected workloads are trusted. Organisations should define which GPU models, firmware versions, drivers and software measurements are acceptable and decide what happens when verification fails. A confidential GPU that has not been properly verified may provide far less assurance than an organisation assumes from the name of the technology alone.
The most useful way to understand confidential AI in 2026 is therefore not as a method that makes a cloud server invisible, but as a method that changes who has to be trusted. The physical server and cloud operator still exist, yet the sensitive workload can be isolated from important parts of the host by hardware-based controls. When confidential CPUs, compatible GPUs, encrypted communication and attestation are correctly combined, organisations can run demanding AI workloads on external infrastructure while reducing unnecessary access to private datasets and proprietary models. That is the central value of confidential GPU computing: powerful AI processing without automatically giving the surrounding host direct visibility into the information being processed.